Cybersecurity Services

Cybersecurity Services That Contain Risk Before Damage Spreads

Web Squalix builds cybersecurity services around the way your software actually runs from cloud workloads and APIs to the devices your teams use every day. Security engineers combine zero trust architecture application security testing and continuous monitoring so weak spots are found and closed before they turn into incidents that halt delivery.

Cloud Security Solutions
We design secure multi cloud environments with identity governance workload isolation and continuous configuration checks so drift is caught early.
Penetration Testing Services
Our testers act like real attackers against your web apps APIs and networks then hand your team clear fixes ranked by business risk.
Threat Monitoring and Response
Web Squalix connects logs endpoints and cloud events into monitored detection workflows that flag suspicious behavior and speed up containment.
Data Privacy and Compliance
We apply encryption key management and access boundaries that support SOC 2 HIPAA and GDPR reviews without slowing product delivery.
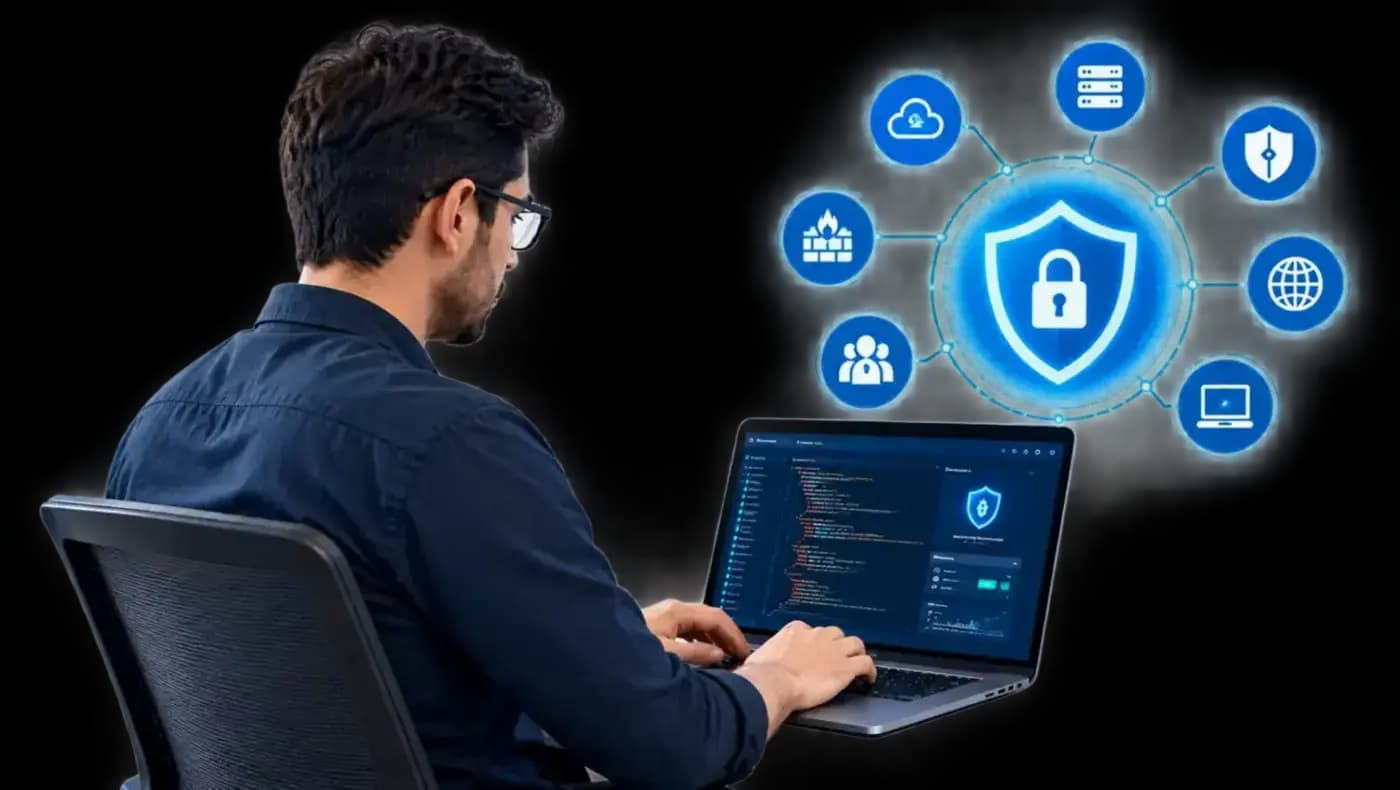
Cybersecurity services illustration showing zero trust architecture protecting cloud infrastructure applications and networks
Avg. delivery
8–12 weeks
Security Engineering

Protecting Business Critical Systems from Evolving Digital Threat Vectors

Attackers no longer break in through one front door. They steal credentials from a forgotten staging server abuse an unprotected API or slip into a software supply chain through a trusted dependency. Traditional antivirus and a perimeter firewall were never designed for that reality which is why ransomware silent data theft and failed audits keep reaching companies that thought they were covered.

Web Squalix approaches cybersecurity services as an engineering discipline rather than a checklist. We start with how your applications users and data actually move then apply zero trust architecture least privilege access and application security testing where the real risk sits. The result is a defense your developers can work with instead of work around.

Because our security engineers also build software we understand release pressure. We bring DevSecOps practices into your existing pipelines document every control in plain language for auditors and executives and stay available after launch so your protection keeps pace with new threats new features and new regulations.

Layered
Defense in depth across every attack surface
Continuous
Monitoring and review after every release
Audit ready
Controls documented for compliance review
Core Capabilities

Practical Defensive Security Solutions Designed for Modern Security Risks

Web Squalix pairs automated threat intelligence with hands on penetration testing services so your cloud platforms web applications and networks are reviewed from both the tooling and the attacker point of view from day one.

Zero Trust Architecture

Applies micro segmentation strong identity checks and device posture rules so a single compromised account cannot move freely through your internal network.

Application Security Testing

Adds SAST DAST and dependency scanning to your existing CI CD pipelines so vulnerabilities are flagged and fixed before code reaches production.

Cloud Infrastructure Security

Hardens AWS and Azure environments with automated IAM privilege reviews continuous posture checking and centralized audit logging your team can trust.

SIEM and Threat Intelligence

Brings log streams from endpoints servers and cloud services together and applies detection rules that surface credential abuse and lateral movement.

Incident Response and Recovery

Provides a prepared response plan and experienced engineers to contain active intrusions trace the entry point and restore services in a safe order.

Endpoint Threat Protection

Watches laptops and mobile devices for suspicious behavior and isolates infected machines automatically so malware cannot spread to shared systems.

Data Encryption and Privacy

Protects sensitive records at rest and in transit through managed encryption keys hardware backed storage where needed and tightly scoped access rules.

Regulatory Compliance Audit

Prepares your architecture and documentation for SOC 2 ISO 27001 and HIPAA reviews with a clear technical remediation plan for every gap found.

Security Use Cases

Proven Security Solutions Protecting Critical Enterprise Infrastructure

Web Squalix designs defenses around strict isolation low false positive alerting and quick recovery. Each implementation is shaped by the assets your business cannot afford to lose or leave unguarded.

Ransomware Defense Systems

Immutable backups and segmented networks that keep encryption malware away from core databases and give you a clean path to recovery.

API Security and Rate Limiting

Traffic filtering and request controls that block bots injection attempts and credential stuffing against your public facing endpoints.

Identity Access Management

Role based authorization that applies least privilege to cloud consoles developer tools and admin panels across your whole organization.

DevSecOps Pipeline Integration

Automated scanning built into build and deploy stages so vulnerable libraries and exposed secrets are caught while the fix is still cheap.

Security Data Lake Analytics

Centralized log collection that correlates large volumes of system events to reveal suspicious insider actions and slow moving attacks.

Supply Chain Risk Mitigation

Vendor code reviews and ongoing access monitoring that reduce the chance of an attacker entering through a third party integration.

Sectors We Protect

Tailored Cyber Security for Highly Regulated Sectors

Web Squalix delivers security solutions for industries where data confidentiality strict compliance and constant availability are not optional for the business.

Fintech
Healthcare
Legal
Retail
Manufacturing
Logistics
Education
Media
Other industries

Custom Solutions Engineered for Diverse Markets

Every industry faces unique digital hurdles. We leverage enterprise technologies, automation, and modern software engineering to streamline workflows and unlock growth, no matter your niche.

Healthcare and Life Sciences

We've built platforms where role-based access and verified identity were non-negotiable. One example is MediFlow, a cloud-native content platform that connects pharma teams with verified healthcare professionals. If your app touches patient data, we design with HIPAA requirements in mind. See our healthcare app development work.

Explore More

Fintech

Secure payment, lending and banking apps. See our fintech app development page.

Explore More

Logistics

Transform logistics operations with AI-powered supply chain and fleet management solutions. Enable real-time shipment tracking, intelligent route planning, and automated warehouse workflows. Reduce delivery costs, improve efficiency, and gain complete operational visibility.

Explore More

Education

Learning apps, student portals and training platforms for universities and professional programs. More on EdTech app development.

Explore More
Case Studies

Security Engagements That Turned Risk Into Measurable Confidence

These representative scenarios show how Web Squalix applies cybersecurity services to problems growing companies face today. Details are generalized to protect client confidentiality.

Fintech

Securing a payments platform before an enterprise audit

The challenge
A growing payments company had to pass an enterprise customer security review but its APIs cloud permissions and logging had grown without a consistent security design.
The approach
Web Squalix mapped the exposed attack surface introduced zero trust architecture for internal services added application security testing to the release pipeline and centralized audit logs.
The business result
The team entered the review with documented controls a clear remediation record and a repeatable process for keeping future releases compliant.
Healthcare

Protecting patient data in a telehealth product

The challenge
A telehealth provider needed stronger protection for patient records across mobile apps APIs and third party integrations while preparing for a HIPAA assessment.
The approach
We introduced field level encryption role based access secure key management and penetration testing services focused on authentication and data exposure paths.
The business result
Sensitive data access became traceable and restricted and the provider gained evidence it could share confidently with partners and auditors.
Retail

Adding DevSecOps to a fast moving retail engineering team

The challenge
An online retailer shipped features weekly yet vulnerable libraries and exposed secrets kept reaching production because security reviews happened only at the end.
The approach
Web Squalix built DevSecOps checks into existing pipelines tuned dependency and secret scanning to reduce false alarms and trained developers to resolve findings quickly.
The business result
Security issues were caught during development rather than after release and engineers kept their delivery pace without extra manual gates.
FAQ'S

Frequently Asked Questions

Straight answers about cybersecurity services, zero trust architecture, penetration testing, and what to expect when you work with Web Squalix.

What do cybersecurity services from Web Squalix include?

Our cybersecurity services cover security assessments cloud hardening zero trust architecture application security testing penetration testing services monitoring and incident response. We scope the work around the systems and data that matter most to your business so you pay for protection that fits your actual risk. You also get a named contact who explains every finding in plain business language.

Why choose a custom zero trust architecture instead of standard off the shelf security tools?

Standard tools rely on generic rules that often miss flaws in your own application logic or cloud APIs. A custom zero trust architecture is designed around your data flows user roles and software stack so access is verified at every step and a stolen password does not open the whole network. That precision also means fewer false alarms for your team.

How are penetration testing services different from a vulnerability scan?

A scan lists known weaknesses automatically. Penetration testing services go further by chaining those weaknesses the way an attacker would to reach real data. Web Squalix testers explain what was reached why it mattered and how to fix it which makes the findings far easier to prioritize. We also retest after fixes so you know each weakness is genuinely closed and not just patched on the surface.

How do I hire cybersecurity engineers for my software project?

Look for hands on experience with cloud defense vulnerability assessment and compliance frameworks plus the ability to communicate with developers. Web Squalix provides dedicated security engineers who join your team review your current setup and build a prioritized plan to harden it. Ask for references from similar environments before you decide and expect clear answers about how engineers are vetted and supervised.

How much do enterprise cybersecurity services usually cost?

Cost depends on the size of your environment compliance targets and scope. A focused penetration test costs far less than a full zero trust architecture rollout with managed monitoring. After the initial review Web Squalix provides a clear scoped proposal so you understand what is included before committing.

Can your team help us prepare for SOC 2 HIPAA or ISO 27001 compliance audits?

Yes. Compliance engineering is a regular part of our work. Web Squalix closes technical gaps enforces encryption and audit logging and prepares the evidence auditors ask for so application security testing results and access reviews are ready when the assessment begins and nothing is assembled in a last minute rush.

What is the difference between security consulting and managed security services?

Consulting delivers assessments architecture reviews and a roadmap. Managed security adds ongoing monitoring patching and incident handling after the plan is in place. Web Squalix offers both so you can start with advice and move to day to day cybersecurity services when you are ready.

How can cybersecurity services help my organization beyond preventing attacks?

Strong security reduces downtime protects customer trust and shortens sales cycles because enterprise buyers increasingly ask for proof of controls. Web Squalix builds cybersecurity services that keep systems available support compliance reviews and give leadership clear reporting on where risk is rising or falling. Reports stay simple enough for non technical stakeholders.

What is application security testing and when should we do it?

Application security testing checks your code dependencies and running software for exploitable weaknesses. The best time is continuously with automated scans in every build and deeper manual reviews before major releases. Web Squalix sets this up so developers receive actionable findings instead of long reports.

How does DevSecOps fit into our existing software development process?

DevSecOps moves security checks into the same pipeline your engineers already use. We add code scanning secret detection and dependency checks to existing build stages tune them to avoid false alarms and train your team on fixes so releases stay fast while risk stays visible without adding slow manual approval gates.

How do we get started with custom Web Squalix cybersecurity services now?

We begin with a focused technical review of your infrastructure access policies and application code. After that you receive a ranked remediation roadmap that shows what to fix first what can wait and what each step is expected to involve in effort and timeline. The review itself is usually short.

How long does it take to roll out zero trust architecture and DevSecOps controls?

An initial audit and urgent fixes can usually be completed in a couple of weeks. A full rollout of zero trust architecture monitoring and DevSecOps automation often takes two to four months depending on how many systems teams and legacy components are involved. We confirm a realistic timeline before work begins.

How do you protect the privacy of sensitive business data stored in cloud platforms?

We combine encryption in transit and at rest managed keys and strict identity controls so only the right people and services can read sensitive records. Regular penetration testing services then verify that these boundaries hold in practice and not just on paper. Findings from each test feed directly into the next hardening cycle.

How should teams prioritise cloud security solutions after a failed audit?

Start with identity and access misconfigurations exposed storage and missing logging because auditors and attackers both target those first. Cloud security solutions then expand to continuous posture checks and network controls once the highest risk findings are closed and evidence can be produced on demand.

Need to harden your enterprise systems? Let's secure it the right way.

Tell us about your product, timeline and goals. You'll get a senior strategist's response within 24 hours.

Confidential, NDA available